Hit by Ransomware? The “Rescue” Company You Call Could Be the Second Scam
Picture this. It is 7:15 on a Monday morning. Every computer in your office shows a ransom note. Your files are locked, your phones are ringing, and your team is standing around waiting for you to say something. You do what almost anyone would do: you search “ransomware recovery” and call the first confident voice that answers.
Last week, federal prosecutors gave every business owner a reason to slow down before making that call.
What happened
According to reporting from The Record, the owner of a Florida company called MonsterCloud has been charged with wire fraud. The company advertised that it could unlock ransomware victims’ files using its own “proprietary tools” and “advanced decryption techniques,” without anyone paying the criminals.
Prosecutors say that was not true. They allege he quietly paid the ransom himself, then billed the victim far more. In one 2023 case, he allegedly paid an $8,200 ransom and charged the client $150,000. Across the scheme, prosecutors say about $19 million was billed to clients while roughly $8 million went to the hackers. He has pleaded not guilty, and these are allegations, not a conviction.
Whatever the court decides, the lesson for you is the same. When you are panicking, you are the easiest customer in the world to overcharge.
Why small businesses are the target
Panic shuts off your questions
When your business is frozen, you will pay almost anything to make it stop. A shady recovery firm knows this. “We have special technology” sounds like a miracle at 7:15 a.m.
You cannot check their work
Most owners cannot tell the difference between real decryption and a ransom payment behind the scenes. That is exactly the gap a bad actor needs.
Paying criminals can create new problems
Paying a ransom is a serious decision. It can raise legal and insurance questions, and it does not guarantee you get all your data back. If someone else makes that decision for you without telling you, you lose control of your own case.
Most recovery firms are honest, and plenty do real work. The point is that you should be able to prove it before you hand over a dollar. And the best defense is not needing them in the first place. Good secure data backups are what turn a ransomware attack from a crisis into an inconvenience.
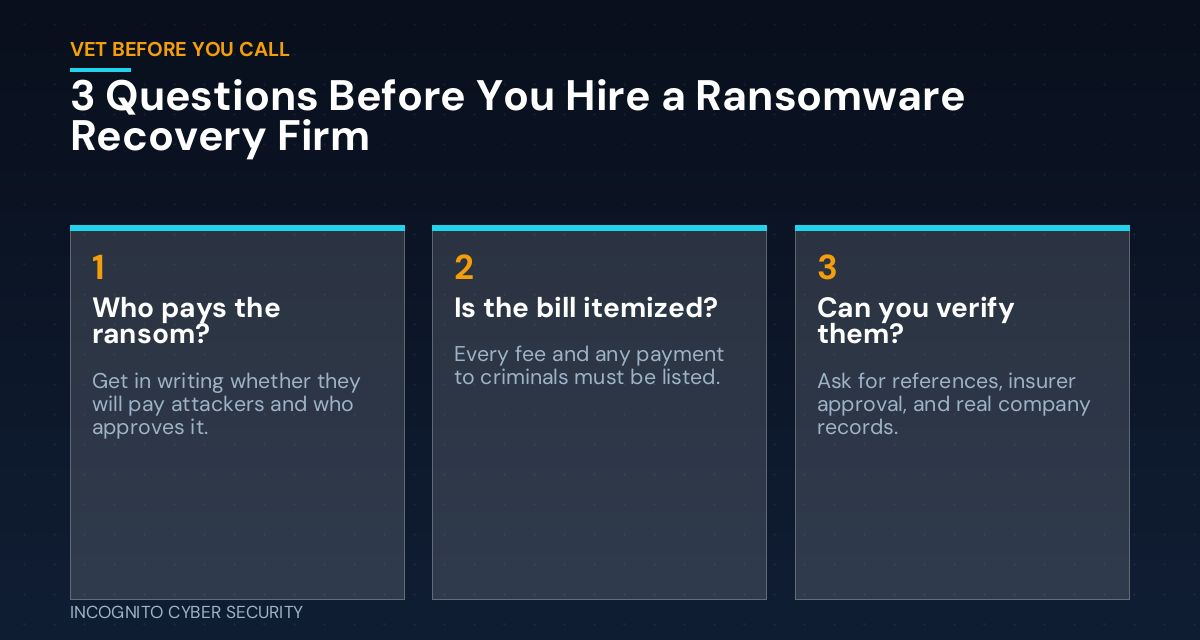
Three questions to ask before you hire anyone
1. Will you pay the attackers, and who approves it?
Ask directly, and get the answer in writing. A trustworthy firm will explain the options, tell you whether negotiation is even on the table, and never spend a cent on your behalf without your clear approval.
2. Can I see an itemized bill?
Labor, tools, and any payment to a third party should each be listed. If the price is a big round number with no breakdown, that is a red flag.
3. Can I verify who you are?
Ask for references you can actually call, proof of a real business, and whether your cyber insurance carrier approves of them. Many policies require you to use their approved responders anyway.
What you can do this week
- Test your backups. Pick a file and restore it. A backup you have never tested is a hope, not a plan. See our secure data backups.
- Keep one backup offline. Ransomware hunts for backups that are connected to your network.
- Write down your emergency contacts now. Your IT provider, your insurance claim line, and one vetted incident response contact. Put them on paper, not only on the computer that might get locked.
- Read your cyber insurance policy. Find out who you are required to call first.
- Add protection that stops the attack early. Modern endpoint protection and spam and virus filtering block much of what starts these incidents.
- Train your team. Most attacks begin with one click. Our cybersecurity awareness training helps.
If you want a refresher on what to do in the first hours of an incident, I wrote about it in One Employee Click Exposed 1.3 Million Arizonans. You can also browse more plain-English articles on our blog.
The bottom line
A ransomware attack is bad enough without being taken advantage of while you recover. Know who you will call before you need them, ask the three questions above, and keep backups that actually work. If you want help with that, our small business cyber security solutions are built for owners exactly like you.
Hit by ransomware, or want to be ready before it happens?
Call us first. We will tell you plainly what we will and will not do, and you will get everything in writing.
Send us a message
Source: The Record, Oct. 8, 2026; This Week in Security, Oct. 11, 2026 edition.
— Nemuel Cruz, Incognito Cyber Security